About us
OMNICOM, Ltd. is a provider of IT management training and also an organization offering consulting services aimed at the development and more efficient functioning of our clients. We have been part of the Slovak market for 30 years, during which time we have trained thousands of participants in our courses and helped improve processes in dozens of organizations. Our consulting services are also used by foreign clients from Europe. The services we provide meet the stringent security requirements in accordance with the ISO 27001 standard.
Our mission
Through professional services and building strategic partnerships in education, consulting and implementation, using world-renowned methods, standards, best practices and tools to help our partners achieve their business goals.
Our vision
An internationally successful team of experts in innovative ways of managing organizations.
Our values
Expertise, flexibility, ethics, value for money, inspiration.

Information Security
OMNICOM operates an Information Security Management System (ISMS) certified to ISO/IEC 27001:2022. The certificate No. 653/24 was issued by SKQS, s.r.o. and is valid from 26 November 2024 to 25 November 2027. The certified scope covers implementation and support services for ITSM/ESM tools.
Our Information Security Policy, approved by company management, sets out how we protect the confidentiality, integrity and availability of our own information and of the information our customers and partners entrust to us. To our customers and business partners we commit that:
- Risks drive our controls. We regularly assess information security risks and apply controls proportionate to the sensitivity and criticality of the information and systems concerned.
- Information is protected throughout its lifecycle. Information is classified, handled according to its classification, encrypted at rest and in transit, and securely returned or deleted when no longer needed.
- Access is limited to those who need it. Access rights are granted based on assigned roles, protected by multi-factor authentication and reviewed regularly.
- Our suppliers meet our standards. Security requirements are part of our supplier agreements, and we rely on cloud providers with recognised security certifications.
- We are prepared for incidents. Security events are reported, assessed and resolved in a defined process, and business continuity plans are tested so that critical services remain available.
- Our people know their responsibilities. All employees and contractors are bound by the Security Policy and receive regular security awareness training.
- We comply with the law. We meet applicable legal, regulatory and contractual requirements, including the GDPR legislation.
- We keep improving. The ISMS is verified by internal and external audits and reviewed by management at least once a year.
To report a security concern related to our services, please use our contact form.
Company management
Miroslav Hlohovský, CEO, Head of Digital

Pavol Holbík, Head of Training Services
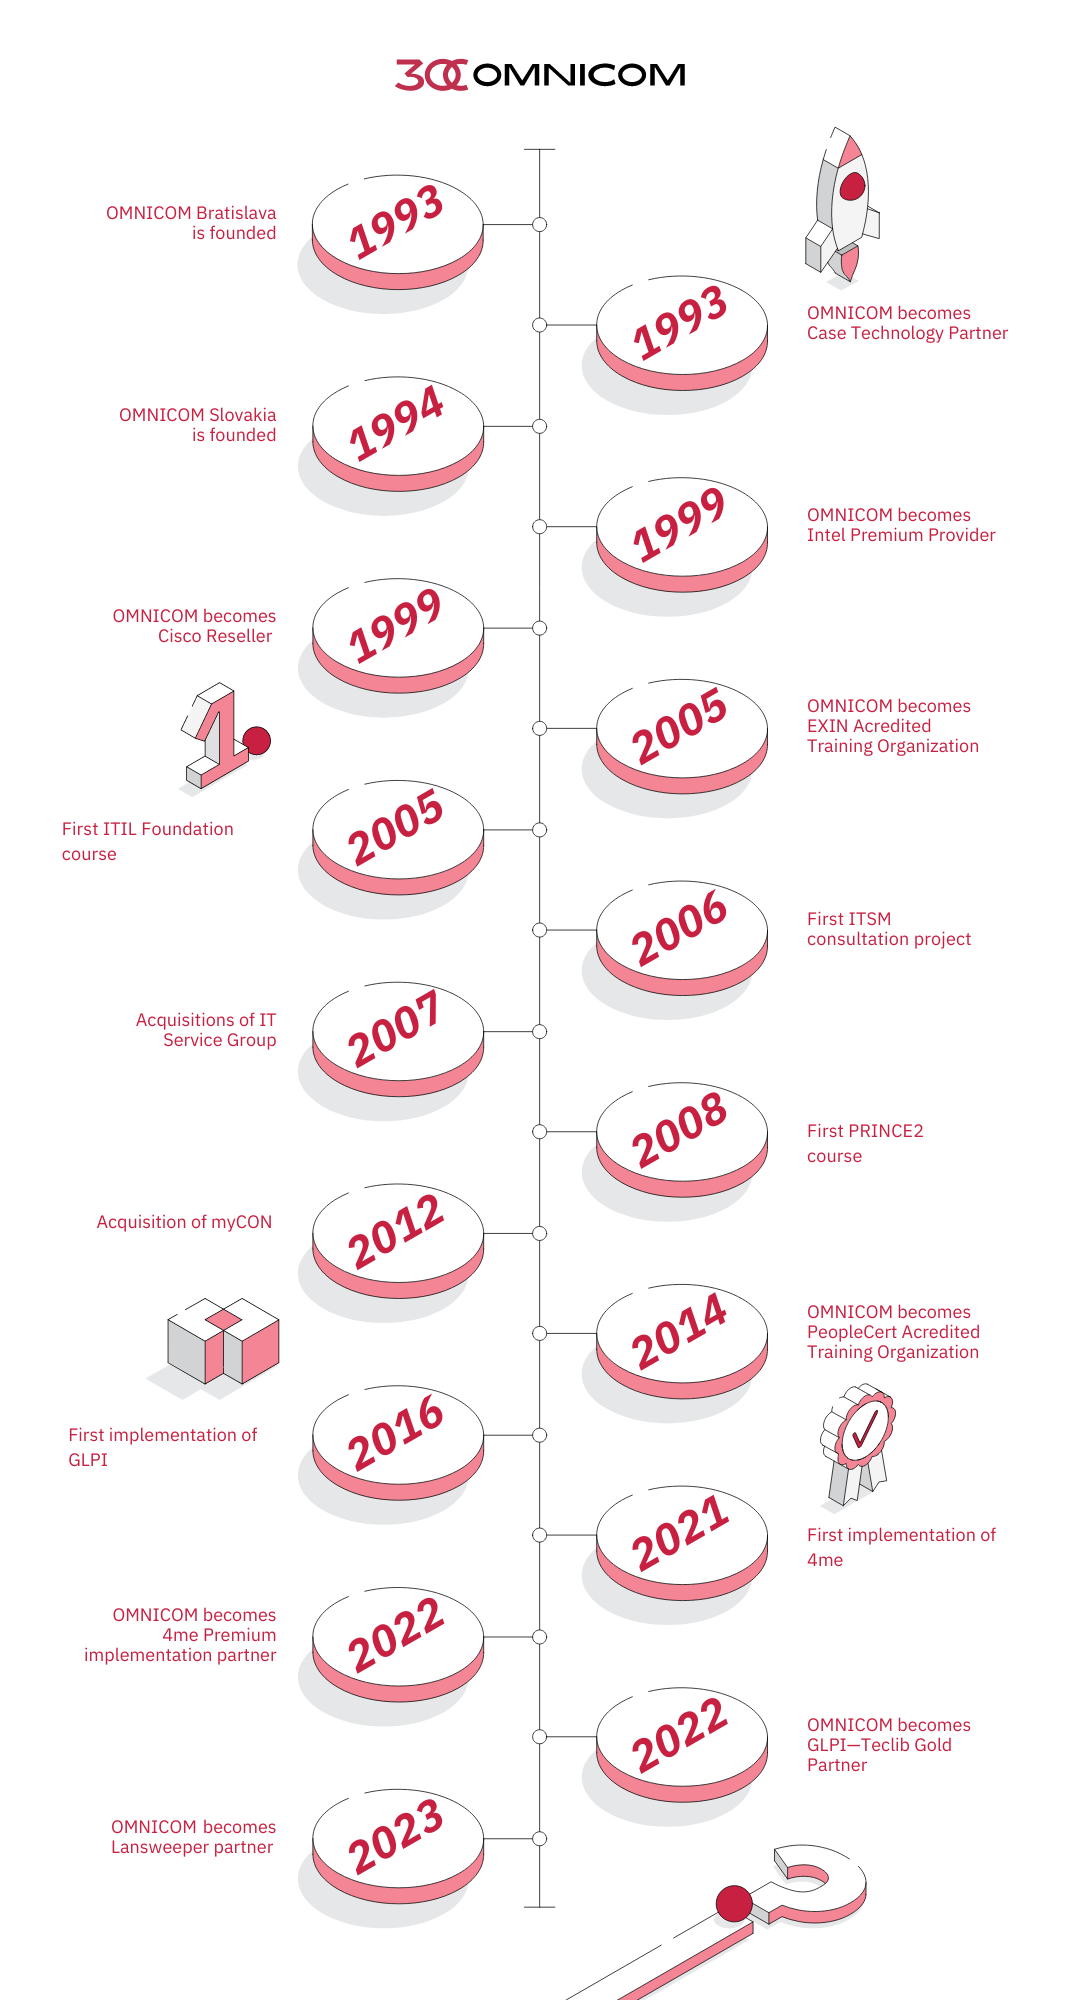
OMNICOM history
OMNICOM’s journey from 1993 to 2023
About company
Business name: OMNICOM, s. r. o.
The company is registered in the Commercial Register kept by the District Court in Bratislava III, section sro, reg. no. 48750/B
Headquarters: Tomášikova 64, 831 04 Bratislava
Business ID: 36 363 383
VAT: SK2022200576
Czech branch
Business name: OMNICOM Consulting & Solutions Czech Republic, s. r. o.
The company is registered in the Commercial Register kept by the District Court in Prague, section C, reg. no. 439947
Headquarters: Plzeňská 3351/19, Smíchov, 8150 00 Prague 5
Business ID: 24365157